
Ocerra now supports Single Sign-On (SSO) with Microsoft 365, so your team can access Ocerra using their existing Microsoft accounts without managing additional logins.
How it works:
1. Set up the first account
An administrator (or someone with authority) logs into Ocerra with their Microsoft 365 email. First, create an Ocerra account using the same Microsoft 365 email. Then log in via “Login with Office 365”. This step activates SSO for your company.
2. Invite other users
Once the admin is connected, other users only need to click “Login with Office 365”. If they are already signed into Windows, they’ll be redirected automatically from the Microsoft page back to Ocerra - no extra login required.
3. Check email addresses
Ocerra matches users by their Microsoft 365 email. If a login fails, Ocerra will display the email address received from Microsoft. Use this to confirm you are inviting users with the correct address.
Enforce Single Sign-On (SSO)
Administrators can require all users to sign in to Ocerra using Single Sign-On (SSO).
To enforce SSO:
Go to General Settings in Ocerra (this setting applies to all integrations).
Locate the Enforce SSO parameter.
Enable the parameter to require users to sign in using SSO when accessing Ocerra.
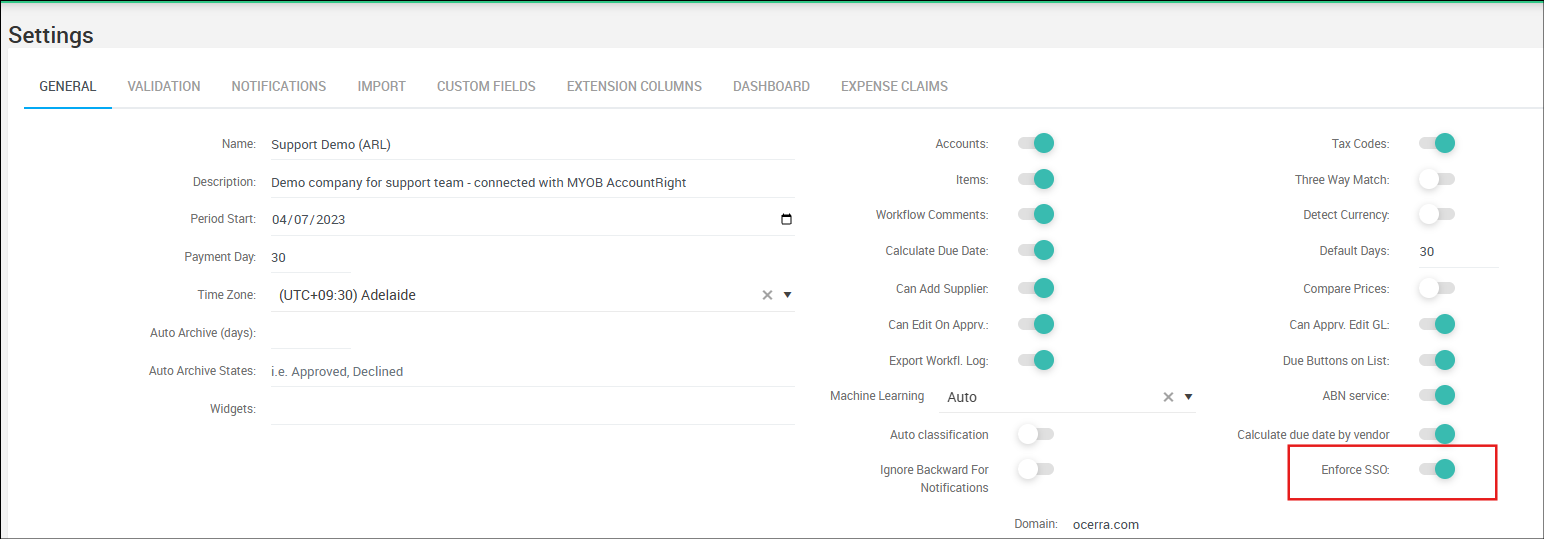
When Enforce SSO is enabled, users must use SSO to access Ocerra rather than signing in using their Ocerra username and password.
Key points to remember
Only the admin needs to activate SSO first.
Each user must be invited with their exact Microsoft 365 email address.
If the email doesn’t match, login will not work.
Enabling SSO with Microsoft 365 makes Ocerra more secure and easier to manage. Access is controlled centrally through your Microsoft environment.